Infrastructure
Healthcare infrastructure and HIPAA safeguards.
Make the flow of sensitive information, the system boundaries and the operating responsibilities explicit.
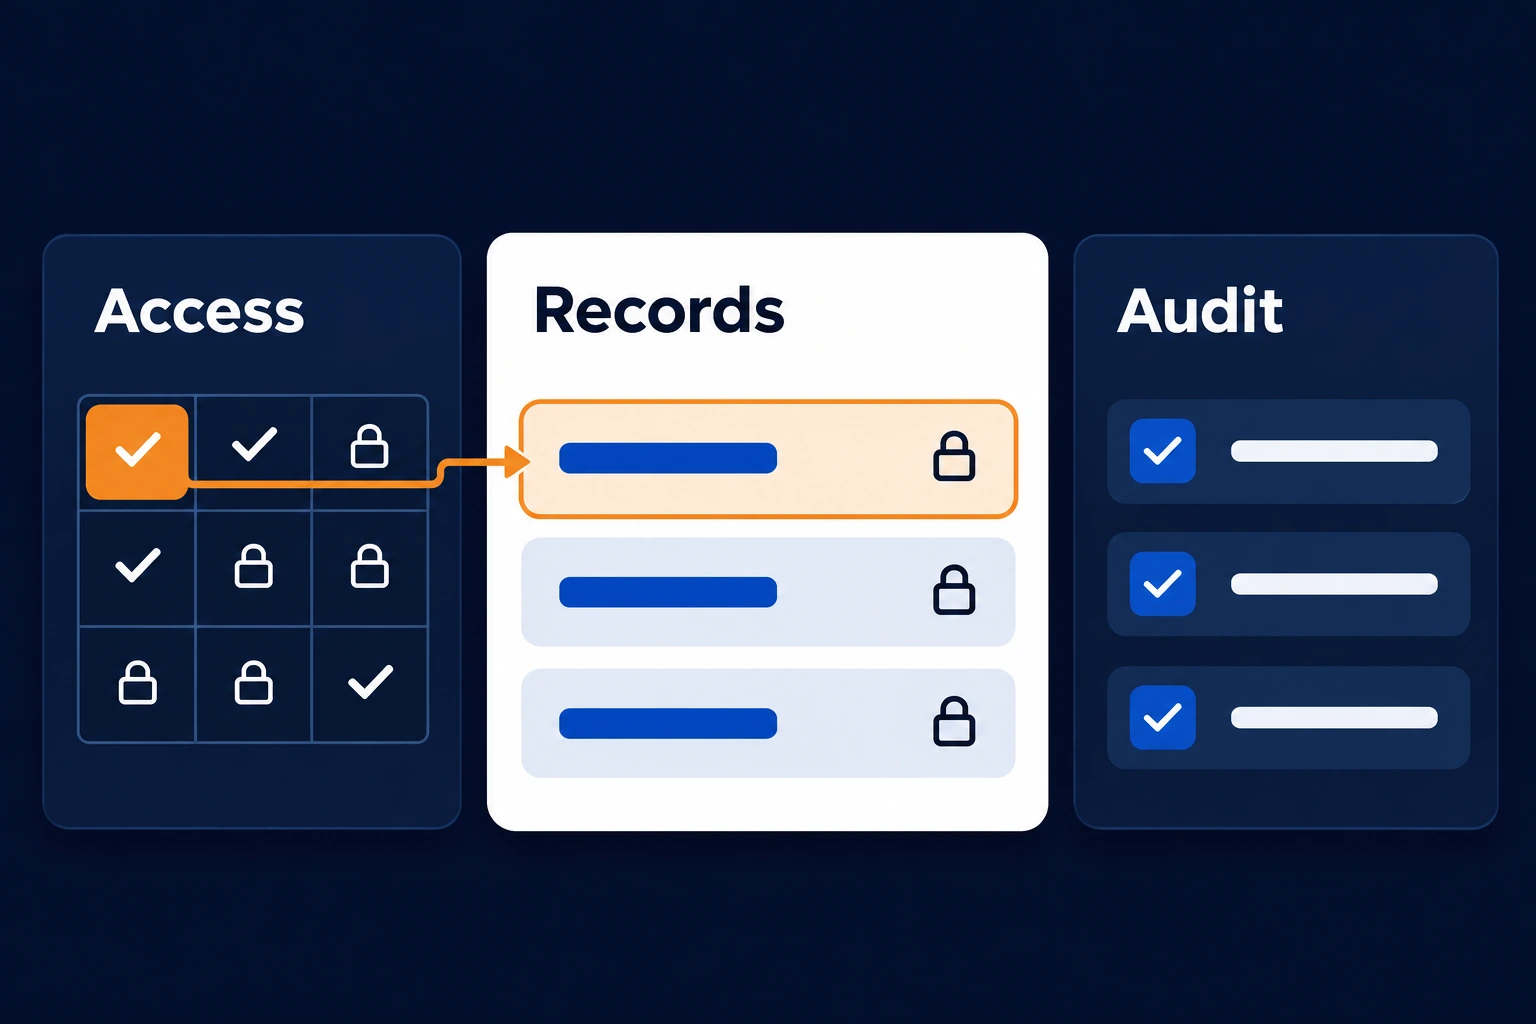
The challenge
The infrastructure diagram is only one part of the picture.
A healthcare system raises questions about where sensitive information travels, who can reach it, which vendors are involved and how the system is operated. Those questions need a shared view of the environment and its responsibilities before technical changes are prioritized.
The approach
Start with the boundaries and the evidence.
Frame the technical review around actual data flows and the safeguards in scope. Coordinate the engineering work with the people responsible for privacy, security and compliance decisions.
Map the information flow.
Identify where sensitive information enters, moves and is stored, including logs, backups and external services.
Review access and responsibility.
Ask who can reach each part of the system, how that access is managed and who owns the relevant operating decisions.
Make safeguards reviewable.
Connect the proposed controls to the identified risks. Define what evidence would demonstrate that the controls work in the environment.
What to verify
An engineering plan that can be examined.
Keep the technical scope, control owners and unresolved risks together. Each safeguard needs evidence that it works in the environment, so the engineering review can inform the people responsible for privacy, security and compliance.
- Data flows and system boundaries are documented.
- Responsibilities and unresolved risks are visible.
- Control decisions are supported by reviewable evidence.